Last week, news emerged that three researchers had hacked into OpenAI using Claude, revealing vulnerabilities in the Sam Altman-led firm.
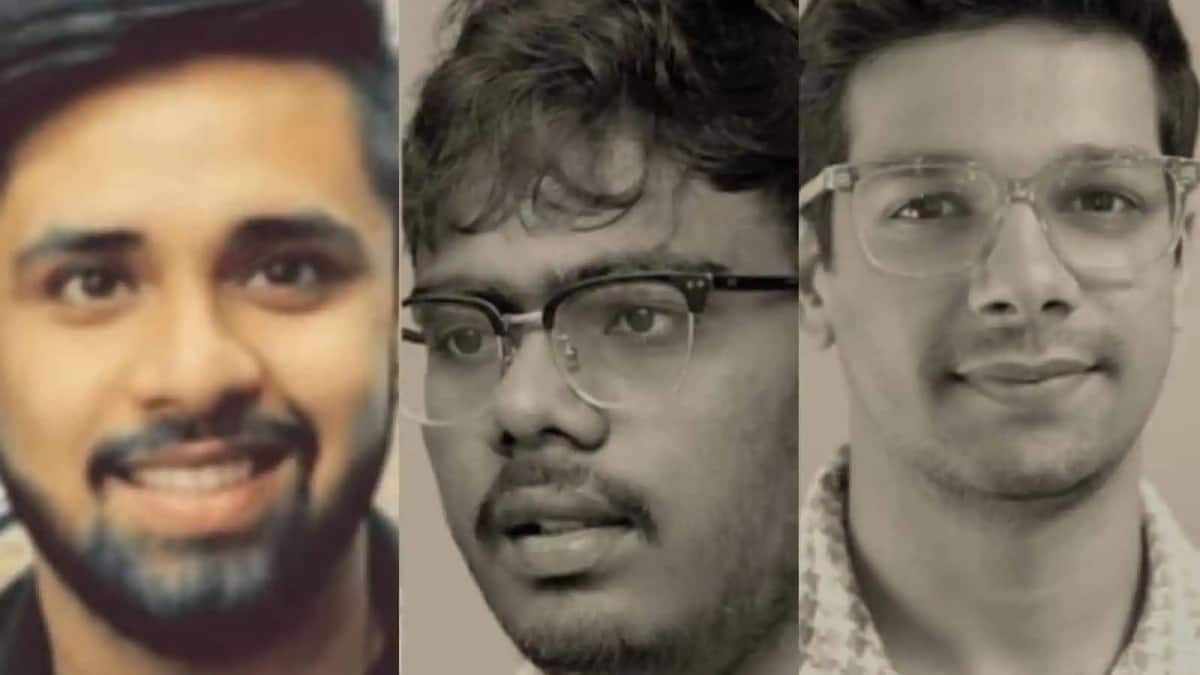
Meet Mohan Pedhapati, Harsh Jaiswal and Rahul MainiAt the heart of the OpenAI hack are three Indian-origin techies who work at cybersecurity startup Hacktron AI.
According to Hacktron AI, Jaiswal led the OpenAI research, with Pedhapati and Maini working with him.
AdvertisementAdvertisementRahul Maini: A graduate in Computer Science, Maini functions as a vulnerability researcher at Hacktron AI.
How the trio made their way into OpenAI using ClaudeJaiswal, Maini and Pedhapati reveal that they got inside OpenAI’s systems with help from the Claude chatbot made by Anthropic.
Last week, news emerged that three researchers had hacked into OpenAI using Claude, revealing vulnerabilities in the Sam Altman-led firm. At the heart of the hack were three Indians: Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini, who work for a cybersecurity startup Hacktron AI. The trio have years of experience in finding serious flaws in the world's largest technology companies, including Apple
In July, shortly after a group of artificial intelligence agents created by OpenAI hacked into Hugging Face, an AI infrastructure company, the ChatGPT maker was a victim of an AI intrusion.
Three hackers used Anthropic’s Claude software to gain access to an OpenAI employee’s ChatGPT account, giving them a way to read and suggest changes to the company’s private cache of software. The three hackers quickly reported their findings to the Sam Altman-led company, following which the trio received a bounty of $6,500 (Rs 6.22 lakh).
While the incident is of note, what makes the story even more interesting is that the three hackers — Harsh Jaiswal, Mohan Pedhapati and Rahul Maini, belonging to the cybersecurity startup Hacktron AI — are of Indian origin.
Advertisement
Advertisement
As the story garners headlines, let’s take a closer look at who exactly these 3 Indian-origin techies are and how they accessed OpenAI’s accounts.
Meet Mohan Pedhapati, Harsh Jaiswal and Rahul Maini
At the heart of the OpenAI hack are three Indian-origin techies who work at cybersecurity startup Hacktron AI. They have several years of experience in finding software vulnerabilities, testing systems, and taking part in bug-bounty programmes. According to Hacktron AI, Jaiswal led the OpenAI research, with Pedhapati and Maini working with him.
What is even more interesting, as Deedy Das, a venture capitalist and partner at Menlo Ventures noted, is that none of the three researchers have “no brand name colleges or companies. Just raw curiosity and skill”.
Harsh Jaiswal: He’s a co-founder of Hacktron AI with his LinkedIn profile stating that he has over 10 years of hands-on experience uncovering critical vulnerabilities across platforms and enterprise applications.
His resume reveals that he has worked as a security engineer and researcher at Project Discovery, Zomato, and Vimeo. He has also participated in bug-bounty programmes through HackerOne. His work has included finding vulnerabilities in products and platforms from companies such as Apple, PayPal, and GitHub.
Advertisement
Advertisement
Rahul Maini: A graduate in Computer Science, Maini functions as a vulnerability researcher at Hacktron AI. He is well known within the community and has worked at the Emirates Group, ProjectDiscovery, and Certus Cybersecurity.
He has also received an AT&T Hall of Fame mention, a Bugcrowd community award, and a first runner-up position at TCS HackQuest 3.0, according to an India Today report.
Around January 2021, Jaiswal and Maini spent months studying Apple’s infrastructure and found a misconfiguration that let them reach protected files without logging in, and ultimately run code on Apple’s systems. For this, they were paid $50,000.
Mohan Pedhapati: Hailing from Andhra Pradesh, Pedhapati is the third researcher in the OpenAI hack. The co-founder and CTO of Hacktron AI, he too is a security researcher.
Before Hacktron, he founded Electrovolt Infosec and worked as a security consultant at Cure53. He also worked as a data science intern at Eigen Vectors, where he explored recurrent neural networks for speech recognition.
Pedhapati, also known online as “s1r1us”, completed his schooling at the Zilla Parishad High School in Sampathnagaram in Rajamahendravaram, and his Bachelor of Technology from Rajiv Gandhi University of Knowledge Technologies, Nuzvid, according to his LinkedIn profile.
A look at the trio’s X accounts reveal the work they have carried out in bug-hunting.
How the trio made their way into OpenAI using Claude
Jaiswal, Maini and Pedhapati reveal that they got inside OpenAI’s systems with help from the Claude chatbot made by Anthropic. After first targeting a public-facing messaging board, they were able to access OpenAI’s private systems, including some of the AI company’s internal code.
They disclosed to The Wall Street Journal that the hack began on July 23 when the researchers were examining OpenAI’s community forum, which runs on Discourse. The researchers found a vulnerability in the way the forum processed certain image files.
The three Indian-origin hackers used Anthropic's Claude to hack into OpenAI in under 72 hours. Representational image/Reuters
Hacktron then used Anthropic’s Claude models to help develop an exploit for the vulnerability. They told the Wall Street Journal that initially their attempts didn’t work. But when Anthropic released Opus 5, they found a way to exploit the bug.
From there, the researchers found another weakness involving OpenAI’s single sign-on system. This allowed them to obtain authentication information linked to ChatGPT and Codex accounts belonging to OpenAI employees.
Advertisement
Advertisement
The trio also accessed OpenAI’s internal code repository, which is significant.
Following the incident, Pedhapati told the Washington Post that the company’s use of conventional business software such as Slack, consumer-grade internet browsers and other apps that are accessible through the public internet, makes it vulnerable to a potential attack.
“If the people building these systems truly believe they are powerful enough to create nuclear-level risks, and they are talking about slowing down because of those risks, why is that work ... done through ordinary SAAS products,” Pedhapati said in a post on X.
Meanwhile, other security experts flag the significance of this hack. Joshua Saxe, the chief technology officer with the AI security company Abundant Security, was quoted as telling the Wall Street Journal that this shows the complexity of defending corporate secrets in the age of AI hacking.
Frank Cilluffo, director of the McCrary Institute for Cyber and Critical Infrastructure Security at Auburn University, also noted to the Washington Post that this should be considered a “warning shot”.
“If three responsible researchers armed with commercial AI tools could achieve this level of access in days, we have to assume well-resourced foreign intelligence services are pursuing the same targets continuously and certainly never tipping off the target about what they did and how,” Cilluffo said.
With inputs from agencies